Company Contact us

Cipher

Secure every identity, govern every interaction

Cipher gives regulated enterprises one identity foundation for customers, employees, partners, applications and machine identities, with a path toward autonomous AI agents.

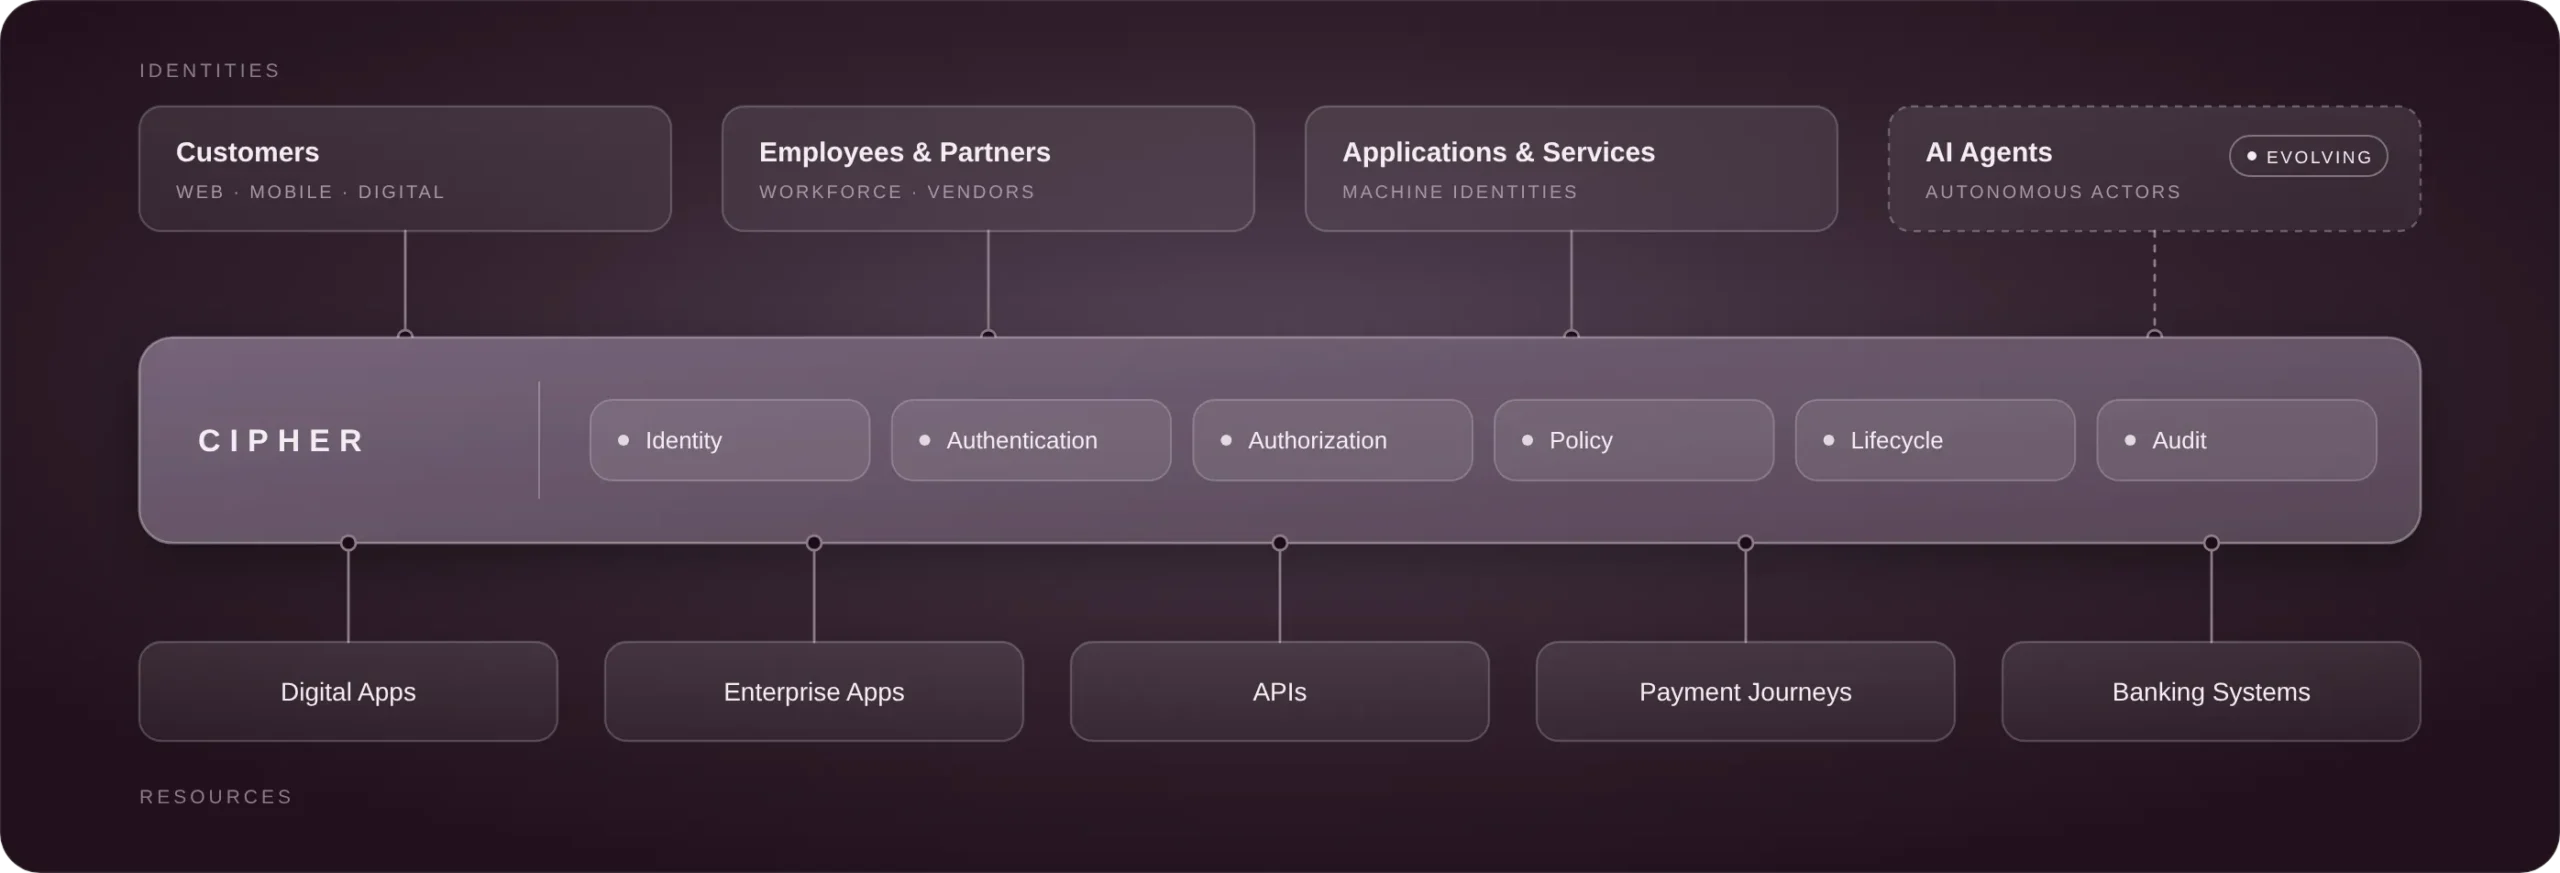
Cipher identity and trust architecture illustration

One identity foundation. Multiple identity domains

Customer IAM

Secure customer access across digital channels with configurable authentication, federation, identity lifecycle and controls.

  • Passkeys, passwordless, MFA and step-up authentication
  • Identity federation and bring your own IdP
  • Customer profile and lifecycle management
  • Registration, recovery, session and journey controls
Enterprise IAM

Manage access for employees, partners, vendors and other enterprise users across applications and services.

  • Enterprise SSO and OIDC / SAML federation
  • RBAC, OBAC and ABAC authorization
  • SCIM-based provisioning and de-provisioning
  • Role, session and access governance

Agent IAM

Give applications, services and processes dedicated identities and credentials, ready to extend to autonomous AI agents.

  • Dedicated machine identities
  • Service-to-service authentication and access
  • Machine credential lifecycle and governance
  • Evolution path toward autonomous agent identity and access
SHARED PLATFORM CAPABILITIES · ONE FOUNDATION
Authentication
Passwordless & passkeys
Identity federation
Authorization
Credential lifecycle
Policy enforcement
Session management
Audit & visibility

Why organizations choose Cipher

Cipher brings the controls required to establish identity, authenticate it, govern what it can access and maintain visibility into its activity, without forcing applications into a proprietary identity stack.

AUTHENTICATION

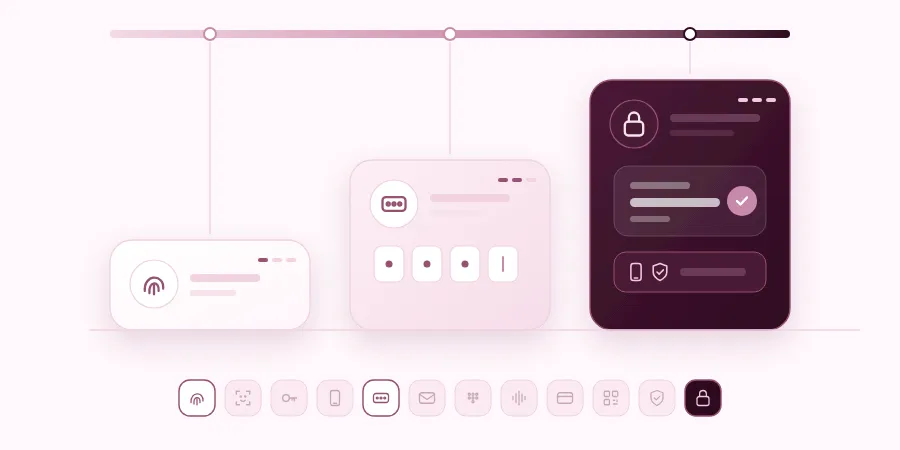
Reduce authentication friction without weakening assurance

Apply the right authentication method to the journey and risk context rather than imposing the same challenge on every interaction.

  • 11+ supported authentication factors across customer and transaction journeys
  • Passkeys and passwordless authentication using device-based verification
  • Multi-factor and configurable step-up authentication
  • Configurable registration and authentication journeys
  • Session management, account recovery, CAPTCHA and rate limiting
Cipher Authentication
AUTHORIZATION

Control access through policy, not application-specific code

Define who or what can access a resource, and what actions it can perform, using centrally managed authorization policies.

  • Role-based, object-based and attribute-based access control
  • Scoped access across applications and resources
  • Just-in-time access
  • Configurable policy enforcement
  • Centralized authorization decisions across identity domains
Cipher Authorization
STANDARDS & FEDERATION

Bring identity protocols onto one standards-first fabric

Connect applications and identity providers using widely adopted standards so identity can evolve without tightly coupling every experience to a proprietary login stack.

  • OpenID Connect and OAuth 2.0
  • SAML 2.0 federation
  • FIDO2 / WebAuthn passkeys
  • Bring your own IdP
  • Headless REST APIs and SCIM endpoints
Cipher standards federation
LIFECYCLE

Govern identity and credentials across the lifecycle

Manage identities, credentials, roles and sessions from creation through suspension, recovery, de-provisioning or removal.

  • Customer profile and identity lifecycle management
  • Enterprise provisioning and de-provisioning
  • SCIM-based lifecycle automation
  • Role assignment and access management
  • Credential, session and notification controls
Cipher Lifecycle
INTEGRATION

Integrate with the identity and risk estate already in place

Introduce Cipher without an all-or-nothing replacement of surrounding identity, application, payment-authentication or risk infrastructure.

  • Bring existing identity providers
  • Integrate through REST APIs, SCIM, OIDC and SAML
  • Use Cipher ACS or integrate Cipher AFA with a third-party ACS
  • Use Zeta risk capabilities or an external fraud and risk-management system
  • Cloud-neutral deployment architecture
Cipher Integration
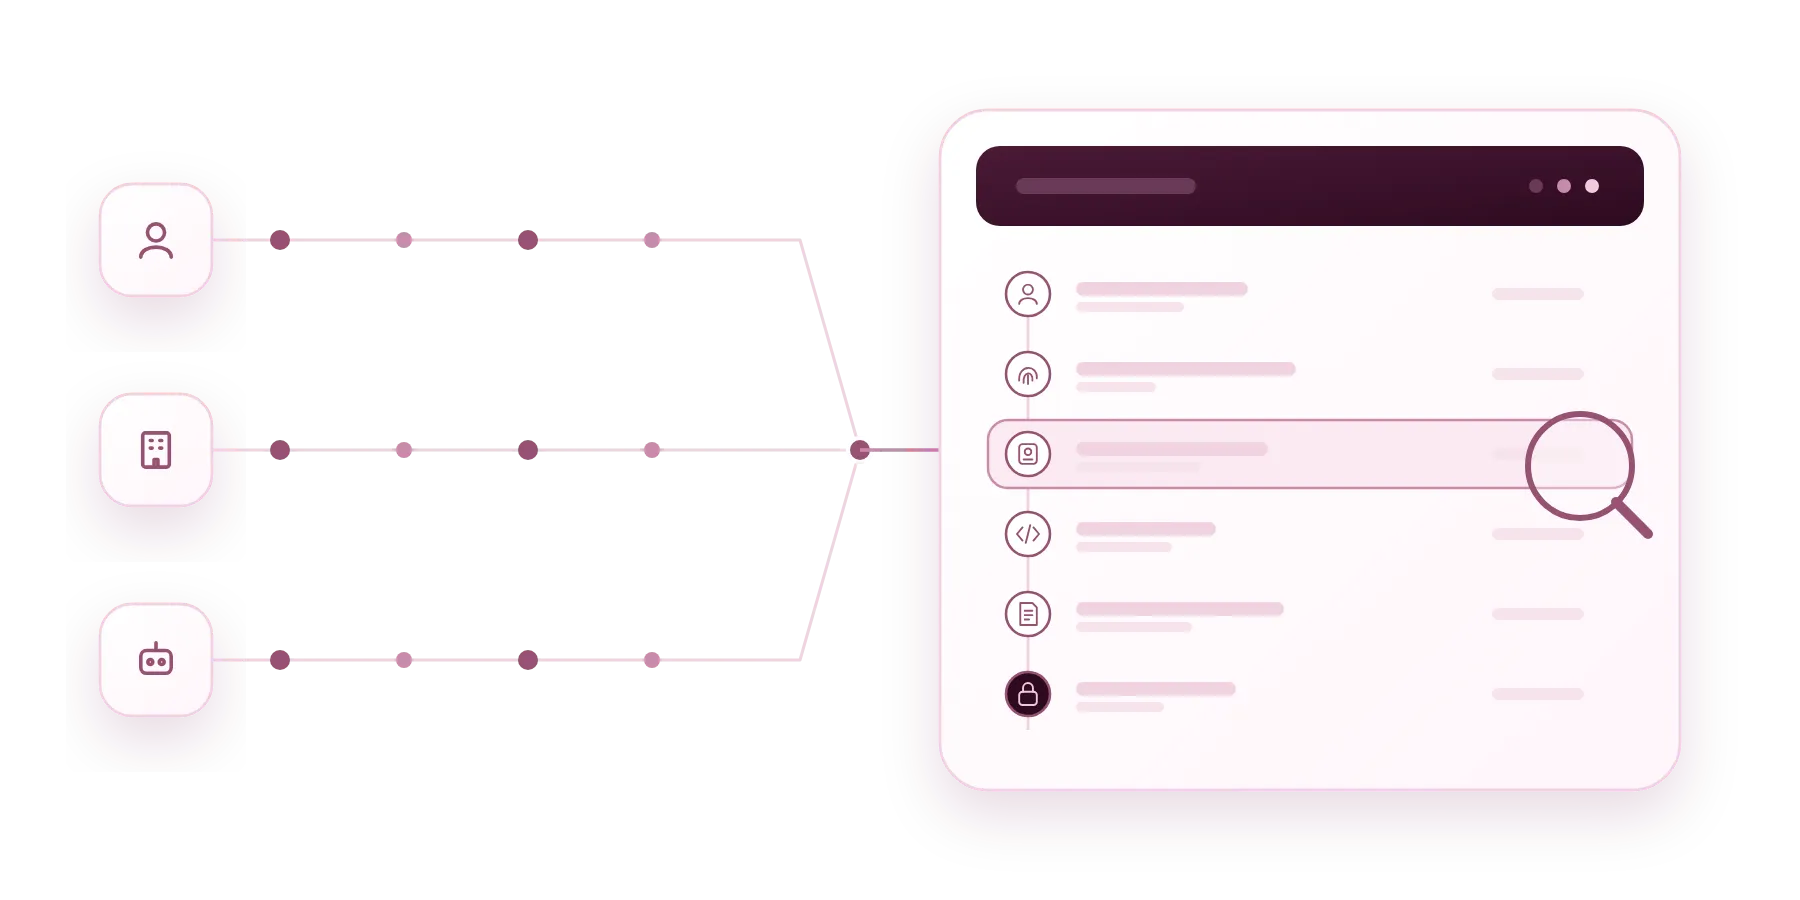
AUDIT & VISIBILITY

Keep identity activity visible and auditable

Maintain visibility into identity, authentication and access activity across customer, enterprise and machine interactions.

  • Authentication and access audit trails
  • Identity and lifecycle visibility
  • Policy and authorization activity
  • Session visibility
  • Centralized logging for security and compliance review
Cipher Audit & Visibility

One platform between every identity and every resource

Cipher Architecture

Move high-risk and payment journeys beyond OTP dependence

Cipher AFA enables passkey-based, device-bound and risk-based authentication across sensitive digital and payment journeys. Users authenticate without waiting for an OTP, while the issuer retains control over when stronger assurance is required. For card payments, it brings passkeys into 3-D Secure using Cipher's ACS or an existing third-party ACS, with decisions informed by Zeta or external fraud and risk signals.

TRANSACTION AUTHENTICATION · DECISION FLOW
Transaction / Action
Risk signals
CIPHER
Authentication policy
Frictionless
Passkey
Step-up
ACS / Application
Authenticated outcome
Dashed elements are valid third-party integration paths. Cipher AFA works with the payment-authentication stack already in place.

Authentication capabilities

  • Passkeys and passwordless authentication
  • Multi-factor and step-up authentication
  • Transaction authentication
  • Device-bound authentication
  • Risk-based authentication

Works with the existing payment-authentication stack

  • Cipher ACS or third-party ACS
  • Zeta or external fraud and risk-management systems
  • 3-D Secure payment journeys
  • Phased migration from OTP to phishing-resistant methods

Standards-first. Proven at identity scale.

Cipher is designed for regulated, high-volume environments where identity infrastructure must remain interoperable, observable and available under continuous load.

725MIdentities stored
806MAuthentication requests served
99.7%Login authentication success rate
3BTokens
5MRoles managed
9MToken verifications per day

Secure every identity, govern every interaction

Schedule a demo