


Choose the infrastructure
Deploy on any public cloud or bank-dedicated cloud instances according to institutional and regulatory requirements.
Olympus
A portable, multi-tenant foundation that standardizes how mission-critical banking software is built, secured and operated across cloud environments.
One operating foundation
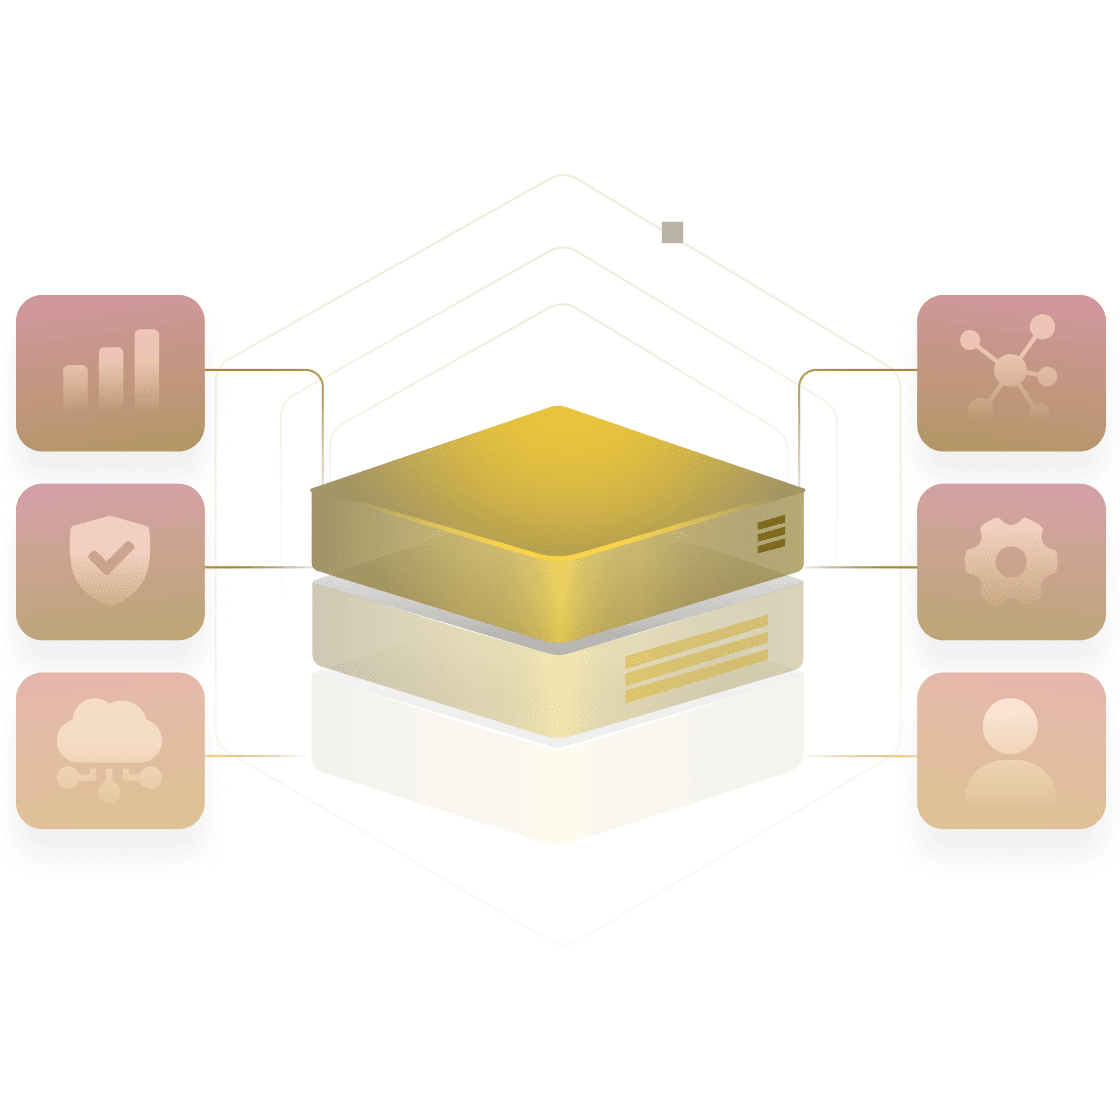
Olympus brings infrastructure, deployment automation, compute, identity, APIs, events, data, observability, security and recovery into one shared platform, giving every banking application a consistent, governed foundation to build, deploy and operate on.
Develop against standardized platform services, integration patterns and operational conventions rather than reinventing the foundation for every application.
Create environments and release software through repeatable, policy-governed automation.
Operate cloud-native workloads on an elastic, resilient runtime designed for transaction-intensive financial systems.
Manage production through a common layer for observability, tenant operations, incidents, security and recovery.
Remove repeated platform engineering from every product program.
Apply common security, deployment and operational policies.
Replace fragmented toolchains with a shared operating model.
Build observability, resilience and recovery into the platform itself.
Banking-grade by design
Olympus was designed around the realities of large-scale banking software.
Built for API-intensive, event-driven and transaction-heavy systems that must combine real-time processing with demanding scheduled and batch workloads.
Deploy across AWS, Azure and GCP-with support for multi-cloud, hybrid-cloud and multi-region architectures.
Separate tenant data, configurations and resources while maintaining common platform standards across environments.
Olympus combines carefully selected open-source and cloud-native technologies with Zeta-built platform services into a coherent operating model. Teams get the benefits of open standards without independently selecting, integrating and operating dozens of underlying technologies.
Cloud agility without giving up the reliability, controls and operational discipline expected of financial infrastructure.
The Olympus platform
Olympus productizes the capabilities required to run distributed financial systems and makes them available through one operating foundation.
Create environments, provision cloud resources, deploy applications and manage change through automated, repeatable workflows.
Connect applications and ecosystems across synchronous APIs, asynchronous events, files and operational workflows.
Operate distributed deployments and automate the lifecycle of tenants, subscriptions, configurations and underlying resources.
Move operational and transactional data from source systems into governed structures ready for reporting, analytics and intelligence.
OAuth2/OIDC · Adaptive policies · Multi-tenant access controls · Auditability
Zero trust · Encryption · Secrets · Policy enforcement
Monitoring · Tracing · Log analytics · Service health
Deployment model
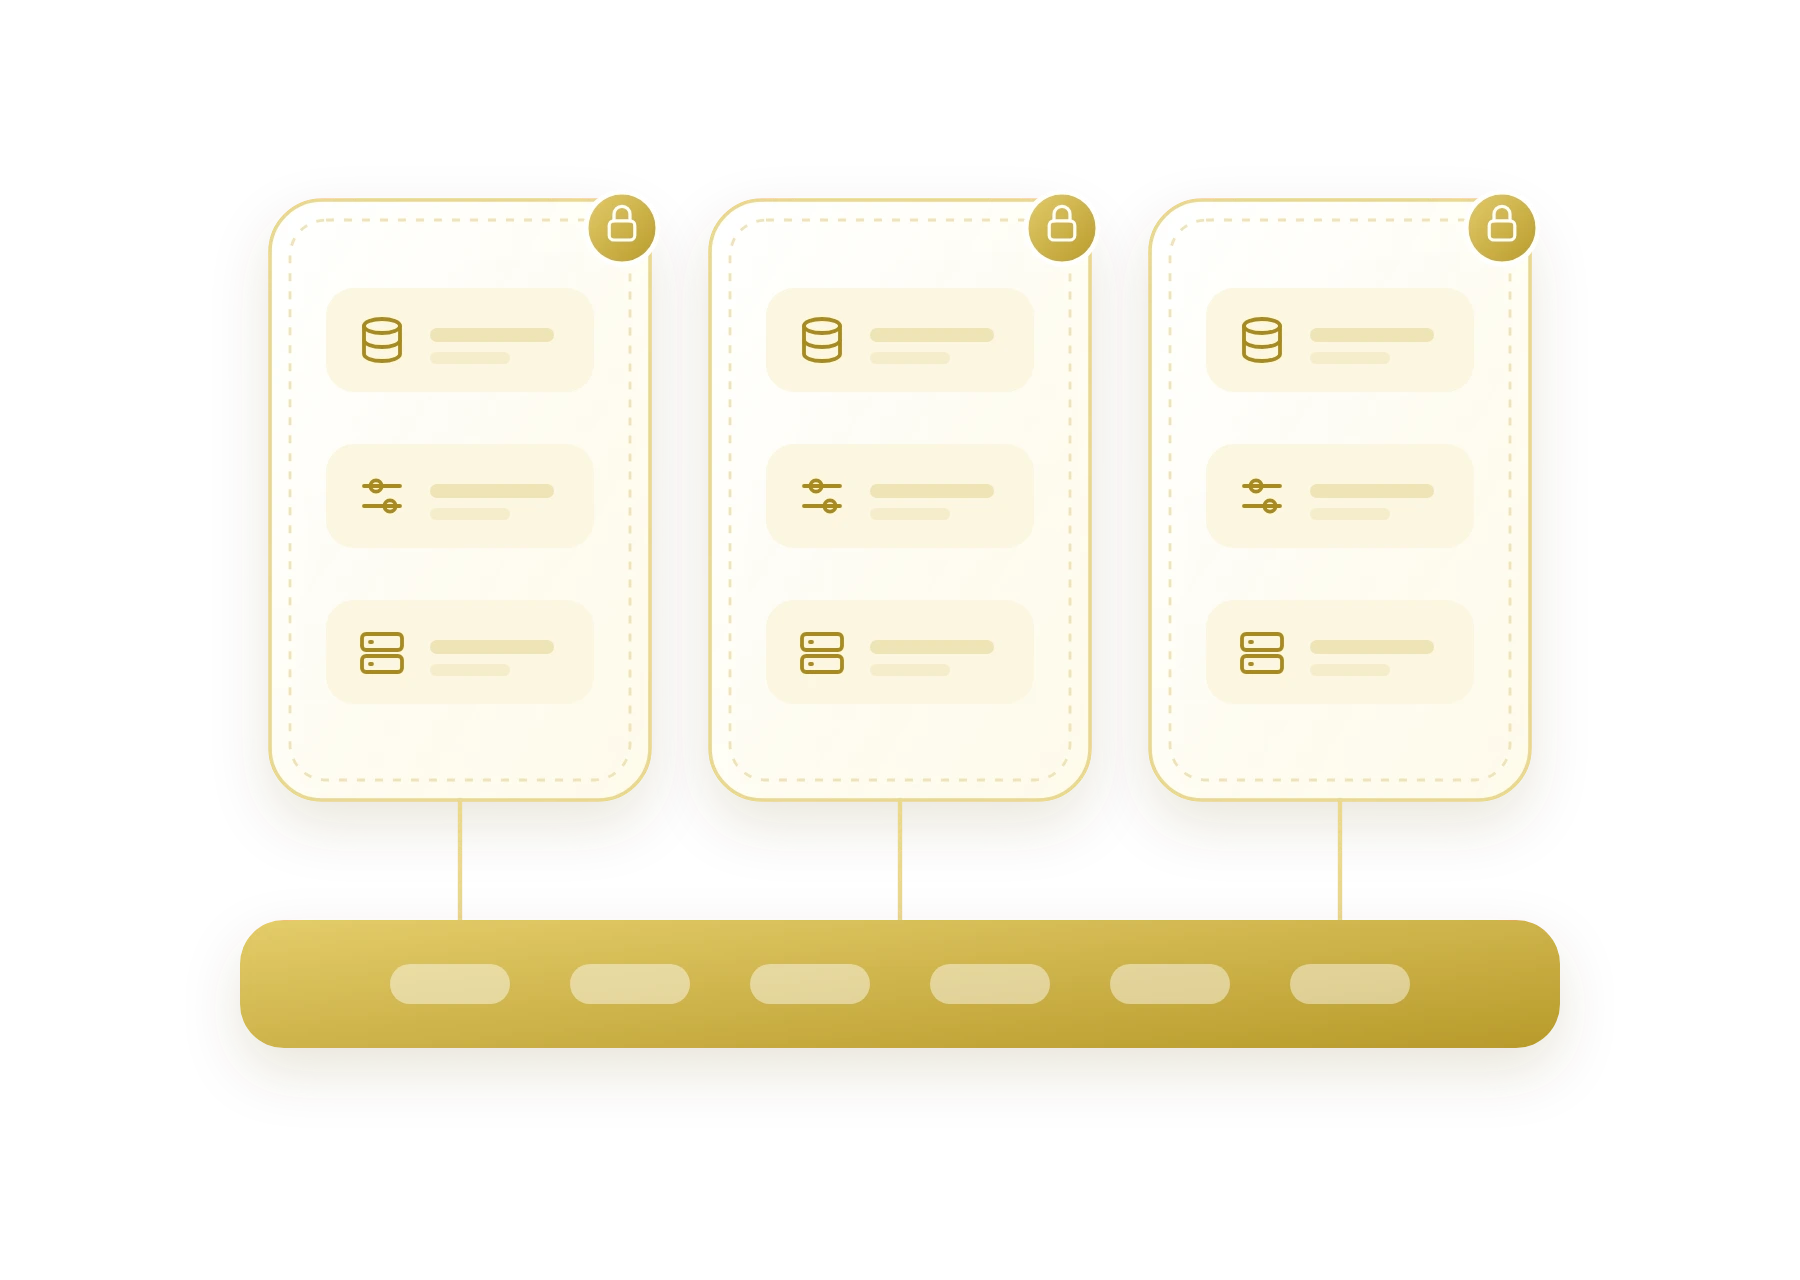
Olympus uses repeatable deployment blueprints to create secure operating environments across accounts, regions and cloud providers.
Each tenant can maintain isolated data, configuration and product resources while inheriting the same infrastructure, security and operational standards.
Deploy on any public cloud or bank-dedicated cloud instances according to institutional and regulatory requirements.
Separate tenant resources, configurations and data planes to contain faults and maintain clear security boundaries.
Coordinate infrastructure resources, business configurations, product resources and SaaS subscriptions through one lifecycle.
Support tenant- and market-specific configurations while retaining a common platform architecture and operating model.
Zero-Trust Security
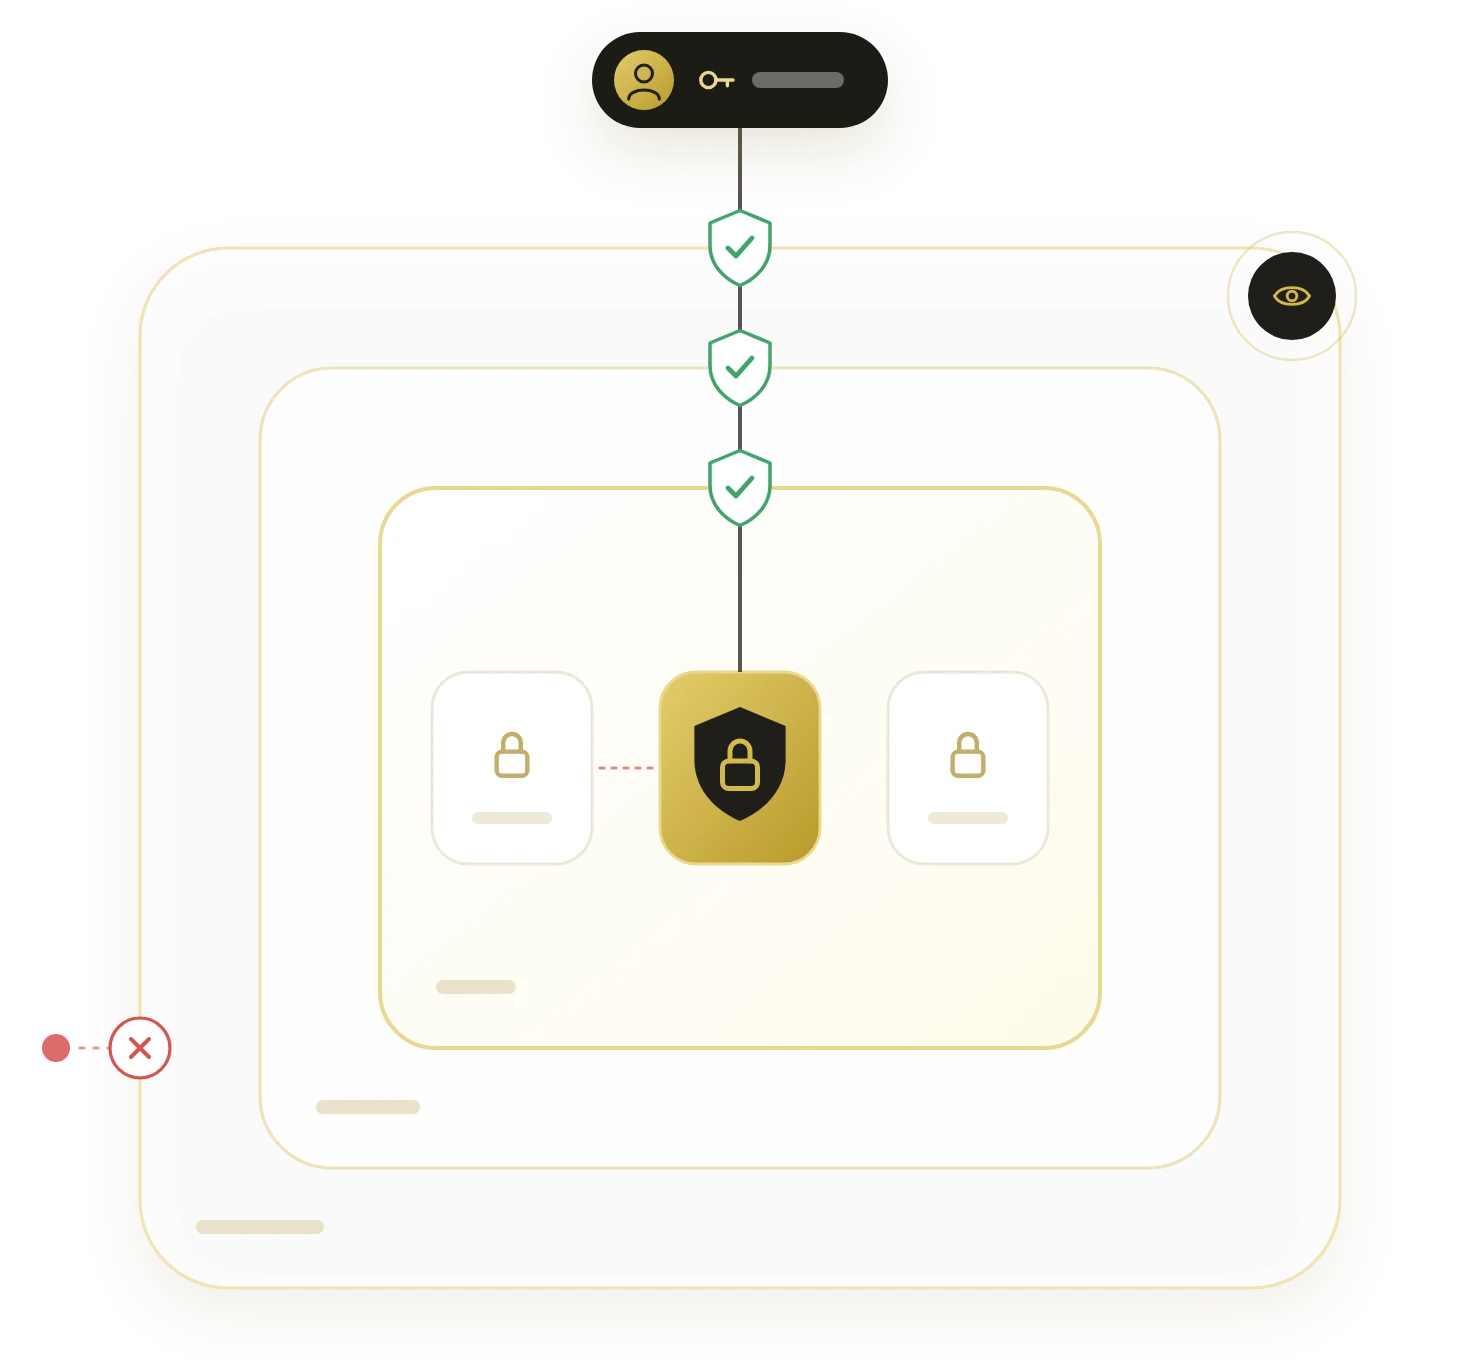
Olympus applies zero-trust principles across identities, devices, networks, applications, workloads and data, combining continuous verification, granular access controls, layered network security and continuous monitoring into the operating foundation.
Strong authentication, federated identity, adaptive access policies and continuous authorization govern access for users, applications and services.
Security controls extend from cloud and tenant networks through hosts, containers and individual workloads, reducing the attack surface and limiting lateral movement.
Security starts before production. Artifacts are scanned, signed and validated through the delivery lifecycle, with immutable infrastructure and continuous vulnerability scanning reducing deployment risk.
Integrated visibility, orchestration and governance provide continuous insight into security posture, policy compliance and emerging threats across the platform.
An AWS case study documents how Zeta implemented its zero trust architecture using AWS security services, open-source technologies and Zeta-built security capabilities.
The implementation combines services including AWS Security Hub, Amazon GuardDuty and AWS IAM with Zeta capabilities such as Cipher and additional open-source and proprietary security controls. This shows how the Olympus security model can be adapted to a bank's security, regulatory and infrastructure requirements.
Read the AWS case studySecurity operating at scale
Observability & Resilience
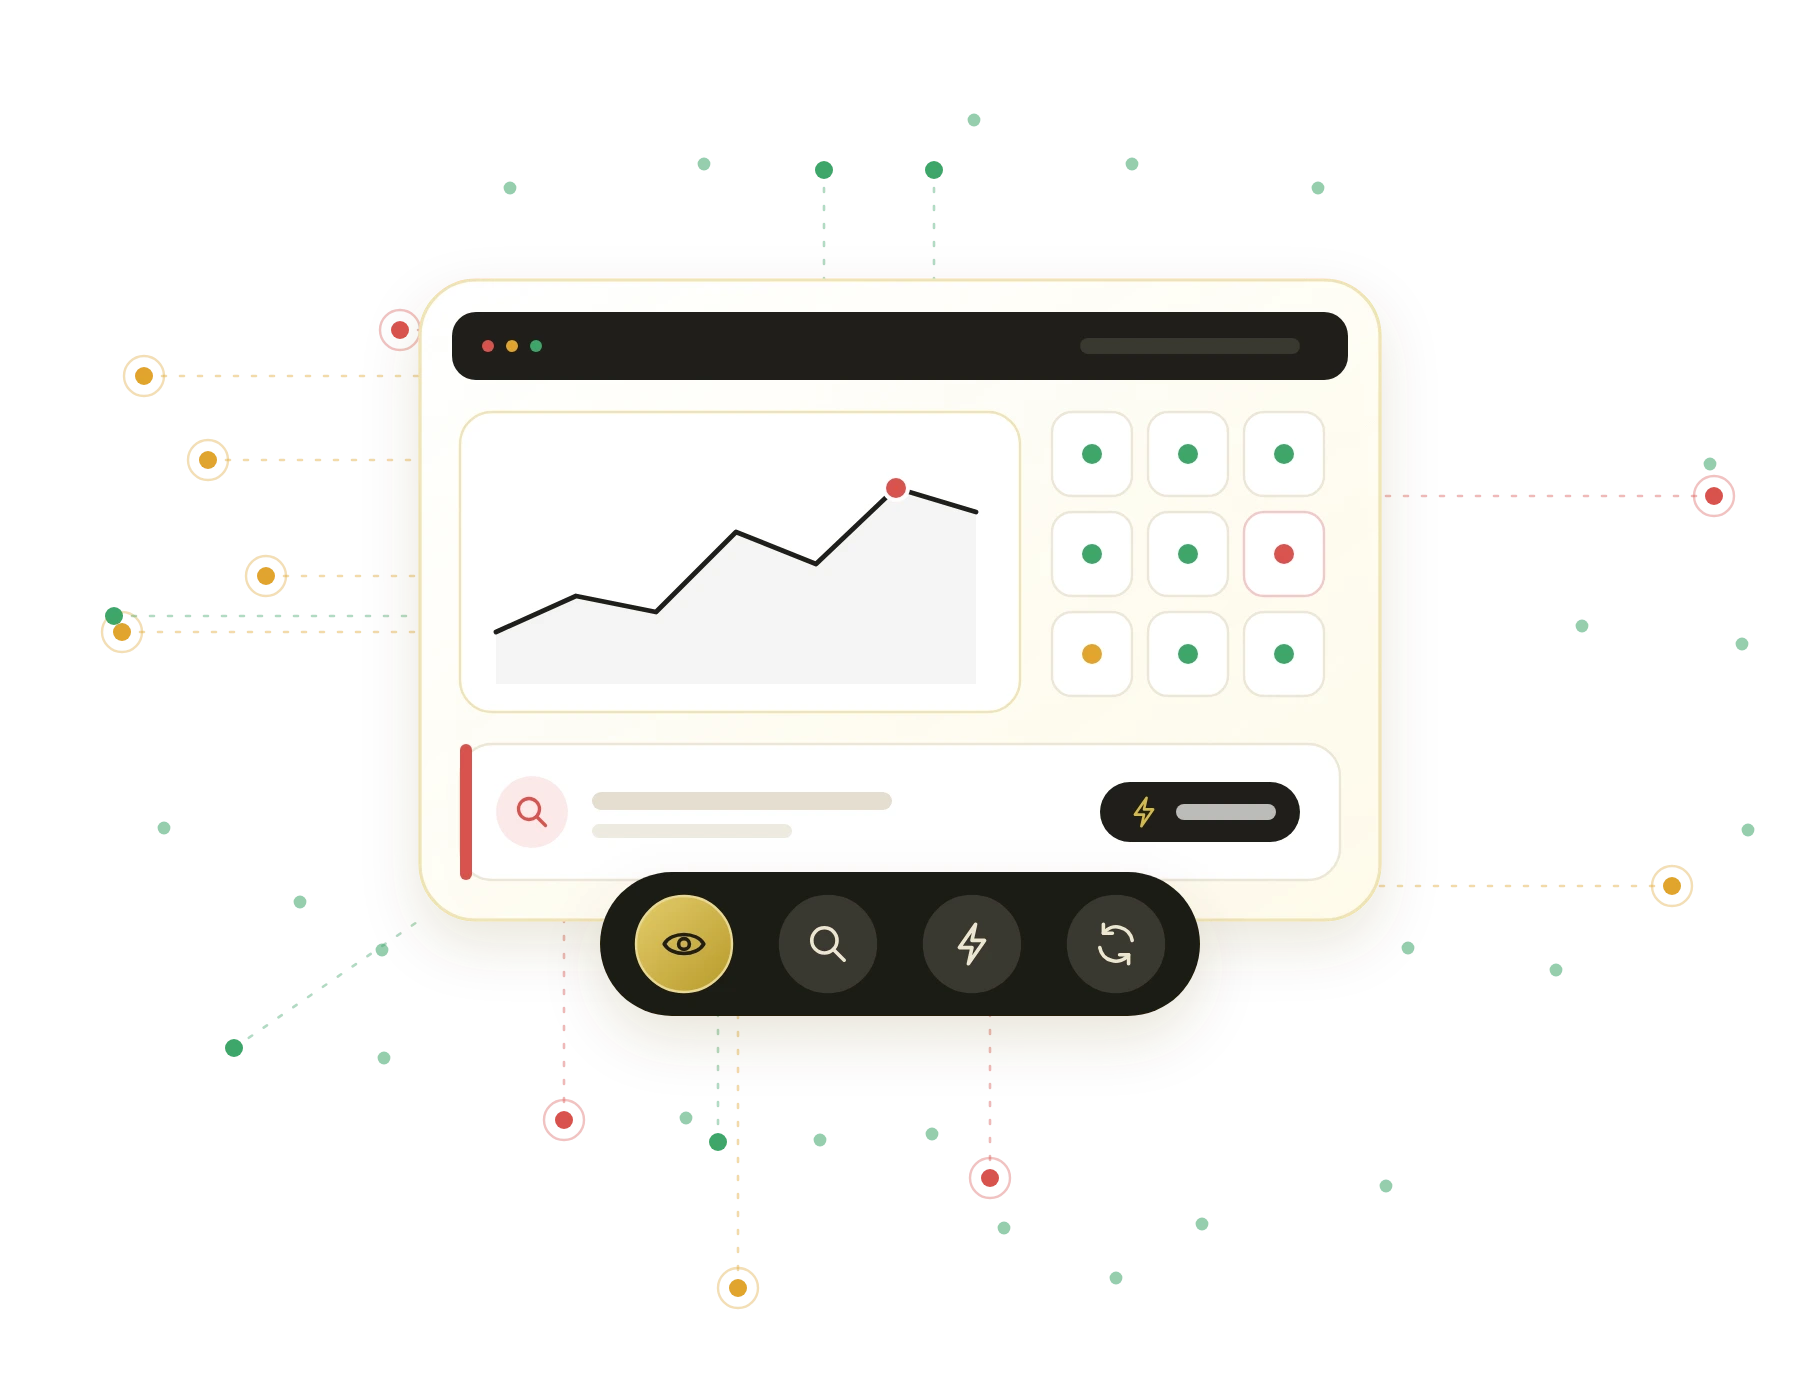
Olympus provides end-to-end visibility across infrastructure, applications, services and customer journeys, combining correlated observability, operational automation and resilience controls to keep mission-critical banking systems available and recoverable.
Metrics, logs, traces, service health and transaction flows in one operational view, from infrastructure through to customer-facing services.
Correlate signals across services and dependencies to find where failures originate and what they affect downstream.
Known remediation patterns become repeatable actions, cutting manual intervention during production incidents.
High availability, workload scaling, failure isolation and disaster recovery across availability zones and regions.
Proven in production
Olympus is not a reference architecture.
Zeta's banking and payments platforms are built, deployed and operated using Olympus, so every product inherits a common foundation for infrastructure, deployment, integration, security, observability and operations.